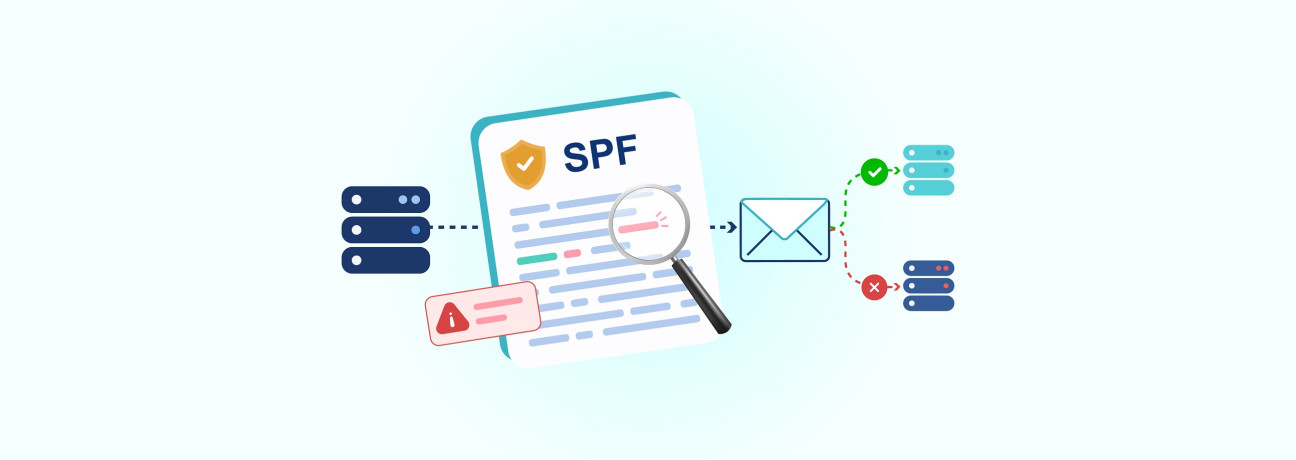
Sender Policy Framework remains one of the most important controls in email authentication , yet it is also one of the most frequently misconfigured. An SPF record tells Mailbox Providers whether a sending server is allowed to send mail for a domain. When the SPF record is wrong, even legitimate campaigns from Google, Microsoft, Verizon-linked infrastructure, CRMs, help desks, or marketing platforms can trigger an SPF failure.
An SPF checker helps expose the quiet problems that damage email deliverability : malformed syntax, missing authorized IP addresses, excessive includes, duplicate TXT record entries, and hidden DNS lookup problems. A good SPF diagnostic tool does more than say “valid” or “invalid”; it shows the SPF status, performs SPF validation, maps the SPF lookup tree, and identifies whether the domain is approaching the 10 DNS lookup limit defined in RFC 7208.
SPF’s Role in Authentication and Spoofing Prevention
Sender Policy Framework supports outbound email authentication by comparing the connecting mail server against the authorized IP addresses listed in the domain’s SPF policy. If the server is approved, the result is typically SPF pass. If not, an SPF failure may occur.
This matters because email spoofing and phishing attacks often rely on forged sender domains. SPF alone does not stop all phishing, but it strengthens email security when combined with DKIM and DMARC. DKIM validates message integrity with cryptographic signatures. DMARC uses SPF and DKIM alignment to help domain owners enforce policy and receive SPF reporting or broader domain authentication insights.
SPF Record Anatomy: Mechanisms, Modifiers, and Syntax That Must Be Exact
An SPF record is published as a DNS TXT record inside your domain DNS settings, usually managed through a domain registrar or DNS hosting provider. SPF record syntax is strict: small formatting mistakes can break SPF validation and cause Mailbox Providers to distrust the email sender's identity.
A basic SPF record example looks like this:
v=spf1 ip4:192.0.2.10 include:_spf.google.com include:spf.protection.outlook.com -allThis SPF record says that one IPv4 address, Google, and Microsoft 365 infrastructure are allowed to send for the domain, while all other senders should fail.
Core SPF Mechanisms You Need to Understand
SPF mechanisms define which systems are allowed to send. Common SPF tags and mechanisms include:
- SPF ip4: Authorizes IPv4 addresses.
- SPF ip6: Authorizes IPv6 addresses.
- SPF a: Authorizes IPs from a domain’s A or AAAA record.
- SPF mx: Authorizes mail servers listed in MX records.
- SPF include: References another domain’s SPF record.
- SPF ptr: Performs reverse DNS checks, but is discouraged because it is slow and unreliable.
- SPF all: Defines the default result for everything not previously matched.
Each SPF mechanism can trigger a DNS lookup depending on how it is used.
Tiny Errors With Big Consequences: Typos, Duplicate Records, Lookup Limits, and Misused Includes
Duplicate TXT Records and Broken Syntax
A domain must not publish multiple SPF records. If DNS contains two TXT record values beginning with v=spf1, Mailbox Providers may return a permanent error. An SPF checker will usually flag this immediately with an SPF warning or failed SPF validation.
Common syntax issues include:
- Using include; instead of include:
- Forgetting v=spf1
- Placing all before other mechanisms
- Adding unsupported characters
- Publishing SPF under the wrong host in domain DNS settings
These errors can make a legitimate email sender look suspicious and cause email deliverability problems.
The 10 DNS Lookup Limit
The 10 DNS lookup limit is one of the most common SPF killers. Sender Policy Framework allows a maximum of 10 DNS lookup mechanisms during SPF evaluation. If your SPF record includes too many third-party services, validation may return “permerror.”
How to Run an SPF Checker Audit: Step-by-Step Diagnosis and Interpretation
A structured SPF checker audit turns a vague deliverability issue into a clear risk assessment. The goal is to confirm that the SPF record exists, follows SPF record syntax, stays within the DNS lookup limit, and lists all authorized IP addresses.
Step 1: Locate the Current SPF Record
Start with an SPF record checker tool such as EasyDMARC or run an SPF command-line check using nslookup or dig:
dig TXT example.comor:
nslookup -type=TXT example.comSome administrators refer to DiG with a capitalized name, but the command is typically written as dig. The output should show one SPF record beginning with v=spf1. If no SPF record appears, your SPF setup is incomplete. If multiple SPF records appear, consolidate them into one.
Step 2: Run SPF Validation and Inspect the Lookup Tree
Next, run an SPF test using an SPF checker that performs recursive SPF lookup analysis. Look for:
- SPF status: pass, fail, softfail, neutral, permerror, or temperror
- Total DNS lookup count
- Flattened authorized IP addresses
- Failed includes
- Deprecated SPF ptr usage
- SPF warning messages
- Vendor-specific issues
The SPF validation process should reveal whether your SPF record authorizes all real senders while excluding unknown systems that could support email spoofing.
Step 3: Interpret the Authentication Result
SPF evaluation depends on the connecting IP, the SPF return-path domain, and the published SPF policy. If the connecting server appears in the authorized IP addresses, the result should be SPF pass. If it does not, the result may be SPF failure.
This is where SPF, DKIM, and DMARC must be reviewed together. A message can fail SPF but pass DKIM, and DMARC may still pass if DKIM aligns with the visible From domain. However, recurring SPF failure signals a gap in outbound email authentication and should be investigated.
Fixing and Monitoring SPF Records: Best Practices to Prevent Future Failures
Practical SPF Fixes That Reduce Risk
Start by removing duplicate records and merging all legitimate sources into one clean SPF record. Keep the record concise and vendor-approved. For Google Workspace, use _spf.google.com; for Microsoft 365, use spf.protection.outlook.com. For EasyDMARC-managed configurations, references such as _spf.easydmarc_us._d.easydmarc.pro may appear depending on the managed SPF service in use.
Avoid unnecessary SPF ptr mechanisms. Replace broad authorization with specific SPF ip4 or SPF ip6 entries where possible. Use SPF a and SPF mx only when they are truly needed, because each can add DNS lookup overhead.
Managed SPF can help large organizations avoid the 10 DNS lookup limit by optimizing includes and maintaining a cleaner SPF lookup path. A managed SPF service is especially useful when teams use many email platforms across departments.
Monitor, Test, and Update Before Failures Spread
Create a regular SPF monitoring process. Before adding a new email sender, run an SPF test in a staging checklist. After every SPF update, perform another SPF lookup and confirm SPF validation. Review DMARC reports and SPF reporting for unexpected senders, repeated SPF warning events, and unauthorized traffic.
Strong SPF compliance depends on accurate authorized IP addresses, clean DNS lookup behavior, and disciplined change management. When combined with DKIM, DMARC, and broader email security controls, a well-maintained Sender Policy Framework record helps protect the organization from email spoofing while preserving email deliverability.